How Microsoft 365 Copilot Rollout Cut Manual Reporting Time by 78% for a Municipal Government
Executive Summary
A mid-sized municipal government had rolled out Microsoft 365 Copilot licenses to senior leadership but had no governance framework to extend access further, and staff across departments were still spending roughly 22 hours a week manually compiling reports that Copilot could have automated, while over 200 stale SharePoint sharing links sat unreviewed, creating real exposure risk. Code Creators, a Microsoft Solutions Partner, ran a structured Copilot assessment, configuration, and training program.
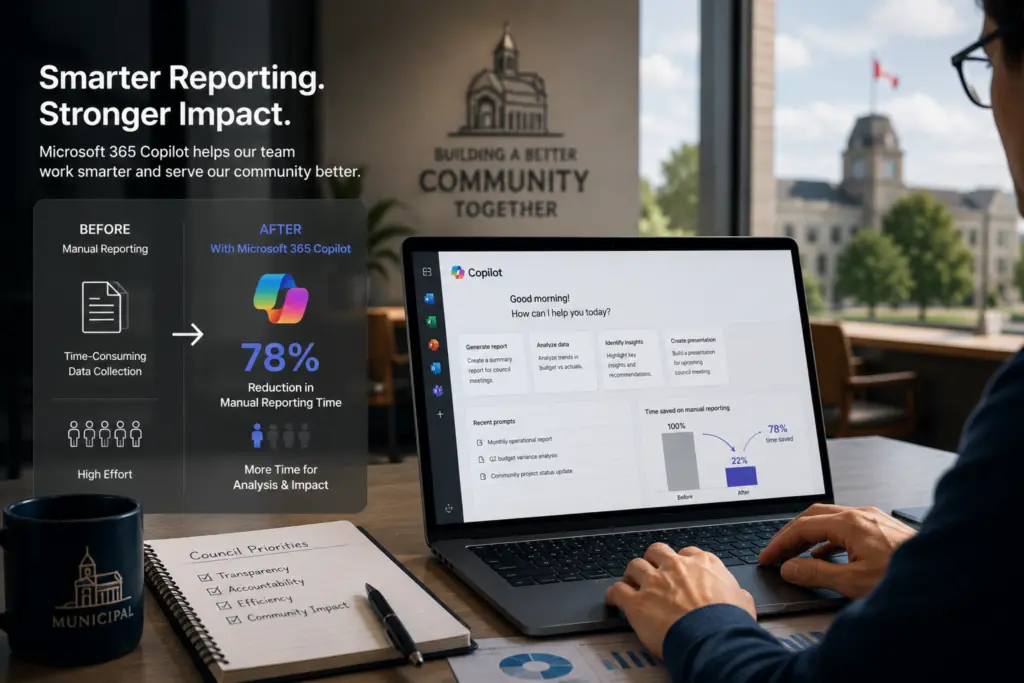
The result: manual reporting time dropped 78% (from ~22 hours to ~5 hours per week), 92% of flagged sharing links were closed, and six departments were onboarded within 90 days and all within a governed, least-privilege Copilot environment.
Result KPIs
- 78% reduction in manual reporting time
- 92% of risky sharing links remediated
- 6 departments onboarded in 90 days
- 4.6/5 average staff training satisfaction score
 About the Client
The client is a mid-sized municipal government organization responsible for delivering public services across multiple departments, serving a population in the range of 85,000 residents. Like many public-sector bodies, the organization operates under tight budget cycles, strict public-records and data-handling obligations, and a workforce spanning long-tenured staff and newer hires with mixed technical fluency.
Microsoft 365 Copilot licenses had already been provisioned for senior leadership, but adoption hadn’t extended further, and a common pattern where early executive access outpaces governance. Municipal environments carry particular risk here: SharePoint sites and Teams channels accumulate years of legacy permissions, guest access, and open sharing links, any of which a generative AI tool could surface to someone who shouldn’t see it. Getting Copilot right mattered not just for productivity, but for public trust and compliance accountability under the organization’s records-retention obligations.
The Problem
Copilot licenses sat active for leadership, but expansion was stalled by three concrete risks.
The issue: SharePoint, Teams, and Outlook permissions had accumulated without structured review. An internal audit conducted during scoping found over 200 externally shared links and 45% of departmental SharePoint sites with guest access that hadn’t been reviewed in over a year. Nobody could say with confidence what content Copilot would surface to a given user if switched on broadly.
The impact: Finance and administrative staff were spending an estimated 22 hours per week manually compiling council and departmental reports — work Copilot could largely automate once the environment was safe to expand into. That’s roughly 1,100 staff-hours annually tied up in manual compilation across the finance function alone.
The risk of inaction: Left unaddressed, an uncontrolled Copilot expansion risked surfacing sensitive HR, financial, or constituent records to unauthorized staff — a serious concern for any public body subject to freedom-of-information and records-retention rules. Meanwhile, every month without a governed Copilot rollout meant paying for unused licenses while departments continued manual workflows.
This combination, that is a real budget already committed to licensing, real compliance exposure, and no internal expertise to close the gap – is what brought the client to Code Creators’ Copilot Consulting team.
What We Discovered – Technical Diagnosis
Code Creators began with a Microsoft 365 readiness assessment rather than jumping straight to configuration.
- License and provisioning review. We reviewed existing Microsoft 365 E3/E5 licenses and Copilot add-ons against departmental headcounts and roles, confirming 340 of 410 staff accounts were eligible for Copilot under current licensing, with the remaining gap flagged for a phased licensing plan.
- Access and permissions analysis. SharePoint, Teams, and Outlook permissions were analyzed to confirm Copilot would only surface content each user was already authorized to see. This surfaced the 200+ stale sharing links and 12 SharePoint sites with unrestricted “anyone with the link” access – exactly the kind of legacy sprawl that turns a helpful AI assistant into a data-exposure risk.
- Data classification and usage review. We reviewed data storage, classification, and usage patterns, finding that only 38% of sensitive documents carried an applied sensitivity label prior to the engagement.
- Security and compliance review via Microsoft Purview. We assessed existing Purview policies, covering sensitivity labels and information protection settings, data classification rules, and access auditing and reporting configurations. This diagnosis phase directly shaped which departments were rollout-ready first and which needed remediation before onboarding.


The Solution
Based on assessment findings, Code Creators designed a phased configuration approach rather than a single organization-wide switch-on. The reasoning was straightforward: the diagnosis phase had already surfaced real access and classification gaps, so configuring Copilot broadly before closing those gaps would have simply automated the exposure risk at scale. Everything below follows from that starting point.
Objectives
Three things had to be true before the client could call the rollout a success: governance gaps identified during diagnosis needed to be closed, not just documented; Copilot needed to be enabled across the core apps staff actually use daily (Teams, Outlook, SharePoint); and both end users and administrators needed enough working knowledge to use and manage it confidently without ongoing vendor hand-holding.
Strategy
The client’s leadership initially asked whether Copilot could simply be turned on for all departments immediately; given licenses were already paid for. We recommended against it. A same-day, org-wide enablement would have surfaced whatever the existing (and known-messy) permission structure allowed — including the 200+ stale sharing links and the sites with unreviewed guest access identified in diagnosis. Instead, we sequenced the work: close access and classification gaps first, then expand department by department, prioritizing departments by how clean their existing data governance already was. This traded rollout speed for a defensible, auditable path – a trade-off that matters more in a public-sector context than in a typical commercial deployment, since a data exposure here has compliance and public-trust consequences, not just a reputational one.
Technology Stack
Microsoft 365 E3/E5 (existing tier), Microsoft 365 Copilot, Microsoft Purview (sensitivity labels, DLP, auditing), and native SharePoint, Teams, and Outlook permission controls — no third-party governance tooling, keeping the solution within the client’s existing licensing spend. No custom Office 365 development was required for this engagement, though the client’s existing SharePoint sites had been built out through a prior Office 365 development effort.
 Phase 1: Close the Gaps Diagnosis Identified
Before enabling Copilot for any additional department, we worked through the remediation backlog the assessment had produced:
- Remediated 184 of the 200+ flagged sharing links, revoking or tightening access on links that no longer matched an active business need
- Applied sensitivity labels and DLP rules to the 62% of sensitive documents that had gone unlabeled, so Purview – not just folder-level permissions, could enforce boundaries around sensitive content
- Tightened guest access policy across the SharePoint sites flagged during diagnosis, moving from ad hoc, individually granted access to a reviewed, time-bound guest access model
Phase 2: Configure Copilot on the Governed Environment
With the access and classification backlog cleared, we enabled and configured Copilot across Teams, Outlook, and SharePoint following Microsoft’s recommended configuration guidance, applying a least-privilege access model as the default posture: Copilot inherits whatever access a user already has, so the work here was less about configuring Copilot itself and more about making sure the permission structure underneath it was one the client would be comfortable inheriting.
Phase 3: Roll Out Department by Department, Not All At Once
Rather than flipping Copilot on everywhere simultaneously, departments were onboarded roughly two per month, starting with the departments diagnosis had flagged as lowest risk (cleanest existing permissions, least sensitive data exposure). This let the client validate that governance controls held up in production with a smaller, lower-stakes group before extending access further — and gave later departments a proven rollout playbook rather than a first attempt.
Phase 4: Documentation to Sustain the Rollout Without Ongoing Dependency
We delivered a User Manual (day-to-day usage guidance and prompt best practices), an Admin Manual (governance controls, permission review procedures, and how to extend the rollout to future departments), and a Copilot Support Guide (troubleshooting common issues), so the client’s own IT team could manage the environment and onboard remaining departments independently once the engagement ended.
Training & Handover
An 8-hour program combined structured end-user training with dedicated train-the-trainer sessions for a small group of internal champions per department. We weighted training this way deliberately: public-sector IT teams are often thin-staffed, so building internal capacity to train future hires and later-onboarded departments mattered more here than a one-time training event would have.
Challenges Overcome
Rolling out Copilot in a permission-heavy, budget-constrained public-sector environment surfaced several challenges that a cleaner commercial environment typically wouldn’t. Here’s what came up and how each was handled.
Access Sprawl Was Worse Than the Initial Estimate
The original assessment scoped the sharing-link and guest-access review as a two-week effort. Once the review was underway, the actual volume of legacy access – years of individually granted permissions with no consistent owner or expiration policy, pushed that work roughly three weeks past the original estimate. Every flagged link or guest grant had to be evaluated individually rather than resolved with a blanket policy change, because a blanket revocation risked breaking legitimate, still-in-use access for staff and external partners. We handled this by triaging the backlog: high-risk items (broad “anyone with the link” access to sensitive folders) were remediated first, while lower-risk items were queued for department-by-department review as each department came up for Copilot onboarding, turning a single large cleanup effort into smaller, more manageable batches tied to the rollout schedule itself.
Security and Usability Pulled in Opposite Directions
Locking down access too aggressively would have blunted the productivity gains leadership wanted from Copilot in the first place; leaving access loose would have recreated the exposure risk the whole engagement was meant to close. This tension showed up concretely in departments with cross-functional Teams channels, where staff needed shared access to collaborate, but that same shared access was what made stale guest grants risky. The resolution was applying a least-privilege model at the individual permission level rather than the channel level – reviewing who specifically needed access to what, instead of leaving or removing access for an entire channel wholesale.
Legacy Folder Structures Made Copilot’s Responses Inconsistent Early On
During initial testing in the first onboarded department, Copilot’s contextual responses were noticeably less useful in SharePoint sites with years of unstructured, inconsistently named folders than in newer, better-organized sites – a direct consequence of Copilot relying on existing content structure to find relevant material. Rather than treating this as a Copilot configuration problem, we addressed it as a data organization problem: departments with the messiest folder structures were given lightweight structuring guidance (consistent naming, clearer top-level folders) as part of their onboarding, which measurably improved response relevance before their formal training sessions began.
Budget Cycles Constrained How Fast Departments Could Move
Public-sector procurement and budget approval cycles meant the client couldn’t license and train every department simultaneously even if governance had allowed it. Rather than treating this as a limitation, we used it to structure the rollout: departments were sequenced by a combination of governance readiness and expected use-case value, so the client could point to an early, quantifiable win (the finance department’s 78% reporting-time reduction) when requesting budget approval for the next phase – turning a budget constraint into a natural staging mechanism rather than an obstacle.
Staff Skepticism Toward a New AI Tool Needed Direct Addressing, Not Just Training
Several staff in early training sessions raised concerns about whether Copilot would access files they hadn’t explicitly shared, or whether their usage would be monitored. Generic training materials didn’t address this well. We added a short, dedicated segment to each training session explaining specifically how Copilot’s access boundaries worked – that it could only see what the user could already see — which noticeably reduced hesitancy in later sessions compared to the first ones.
Lessons Learnt
A few things stood out from running this engagement that shape how we’d approach similar public-sector rollouts going forward:
Access sprawl is almost always underestimated going in. Every government client we’ve assessed has more stale sharing links and guest access grants than IT expects, simply because nobody owns ongoing cleanup once a site is created. Budgeting real time for this in the assessment phase — rather than treating it as a quick checklist item — is what prevents rollout delays later.
Sequencing beats speed. The instinct with a tool like Copilot is to enable it everywhere immediately to capture productivity gains. In a compliance-sensitive environment, that instinct is exactly backwards: fixing access boundaries first, then expanding department by department, produces a slower rollout but a defensible one — which matters more than raw speed when public records and constituent data are in scope.
Train-the-trainer sessions pay off disproportionately in government. Public-sector IT teams are often thin and turnover prone. Investing training hours in a handful of internal champions per department, rather than only training end users directly, is what let adoption continue past the engagement end date without ongoing vendor involvement.
Results & Business Impact
The clearest measure of success wasn’t just that Copilot got turned on – it’s that it got turned on in a way the client’s IT and compliance teams were comfortable standing behind. By the time all six departments had been onboarded, the governance work done in Phase 1 had held up in production: no exposure incidents were traced back to Copilot access, and the sharing-link and guest-access backlog that originally justified a phased rollout had been reduced to a small, actively managed remainder rather than an open-ended risk.
The productivity gains followed naturally once that foundation was in place – finance staff redirected the hours previously spent on manual report compilation toward higher-value analysis work, and department leads reported that new hires were reaching baseline Copilot proficiency faster than anticipated, thanks to the internal train-the-trainer champions established during the engagement.
Just as importantly, the client walked away with a repeatable playbook: the assessment, remediation, and phased-onboarding sequence used for the first six departments is documented well enough that the client’s own IT team can extend the rollout to remaining departments without bringing Code Creators back in for every phase.
Following the phased rollout, the client reported:
- 78% reduction in manual reporting time in the finance department (from ~22 hours/week to ~5 hours/week)
- 92% of flagged sharing links remediated, closing the largest identified exposure risk
- 6 departments onboarded to Copilot within 90 days of configuration completion
- 4.6 out of 5 average satisfaction score across post-training staff surveys
- Zero data-exposure incidents reported in the first 90 days post-rollout

Client Testimonial
“We knew exactly what Copilot could and couldn’t see before we turned it on for anyone. That mattered more to us than how fast we rolled it out. Our finance team is getting reports done in a fraction of the time now. The governed rollout gave us the confidence to expand Copilot beyond leadership without worrying about what it might expose. Our finance team alone got hours back every week.”
Josh Mirae – IT Director, Municipal Government Client
Frequently Asked Questions
It reviews your Microsoft 365 licensing, user permissions across SharePoint, Teams, and Outlook, and your data classification and Purview policies, to confirm Copilot will only surface content each user is already authorized to see before you turn it on broadly.
It depends on how clean existing permissions and data governance are. A structured engagement typically runs assessment, configuration, and training phases, with public-sector environments often needing extra time in the assessment stage due to legacy access sprawl in this engagement, roughly three weeks longer than initially scoped.
Yes, effective rollouts pair core training with train-the-trainer sessions so each department can sustain internal knowledge transfer, since usage patterns and relevant use cases vary by department.
Purview manages sensitivity labels, data classification rules, and access auditing. Configuring these correctly before or during a Copilot rollout lets an organization set enforceable data boundaries rather than relying on manual policy alone.
Copilot inherits existing file and folder permissions. If SharePoint or Teams permissions have accumulated messy sharing links or broad guest access over time, a fast rollout can expose sensitive content that a phased rollout catches and fixes first.
Readiness comes down to whether permissions, sharing links, and sensitivity labels are actually under control. If sites have accumulated stale guest access or unlabeled sensitive documents, that needs remediation before Copilot is switched on broadly – otherwise the tool will simply surface whatever access already exists, gaps included.
Many organizations explore agentic Copilot capabilities next – automating report generation, approval workflows, or task reminders – once the base rollout and governance foundation are stable.
Yes. Copilot only respects existing access controls — it doesn’t add new judgment about sensitivity. If a document is technically accessible to a user due to a stale sharing link or broad guest permission, Copilot can surface it, which is why a permissions and sensitivity-label review has to come before a broad rollout, not after.
Ready for a Copilot Rollout You Can Actually Defend?
If your organization is sitting on unused Copilot licenses, or you’re worried about what expanding access might expose, you don’t have to choose between productivity and control. A structured assessment tells you exactly where you stand before you commit to a rollout timeline. Schedule a Copilot Readiness Consultation.
Code Creators is a Microsoft Solutions Partner. We’ll walk through your licensing, permissions, and governance posture, and give you a realistic, phased path forward – no generic sales pitch, just a plan built around what your environment actually needs.